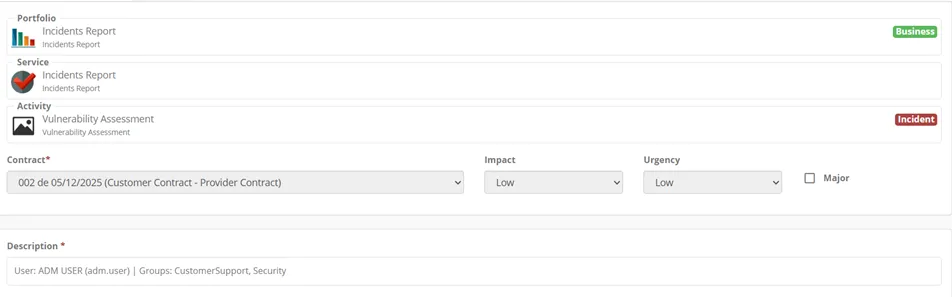
GRC
The platform achieved the ITOM process and use the monitoring and event system for gather all events and create correlations based in specific business rules including Ai Autonomous agents and create incidents if needed.
The event center gather all information from external platforms like SIEM, XDR, APM and self-agents
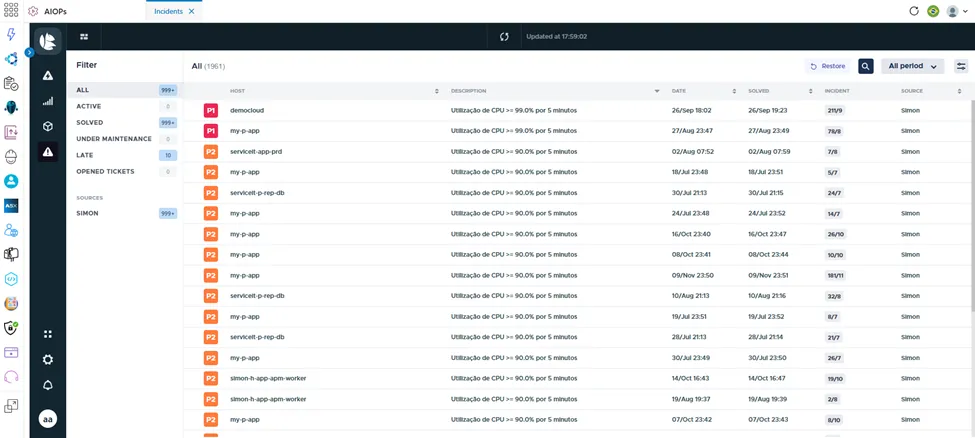
Based on business rules can open an incident and do the scalation automatically including cooperative communication.
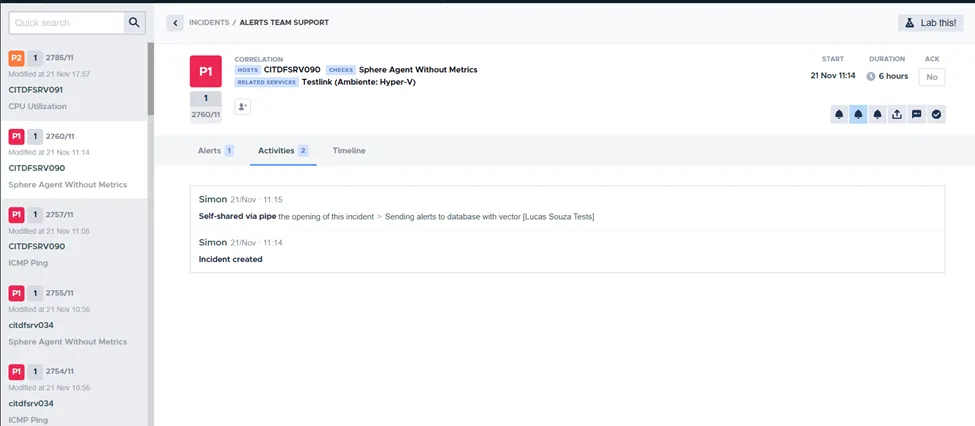
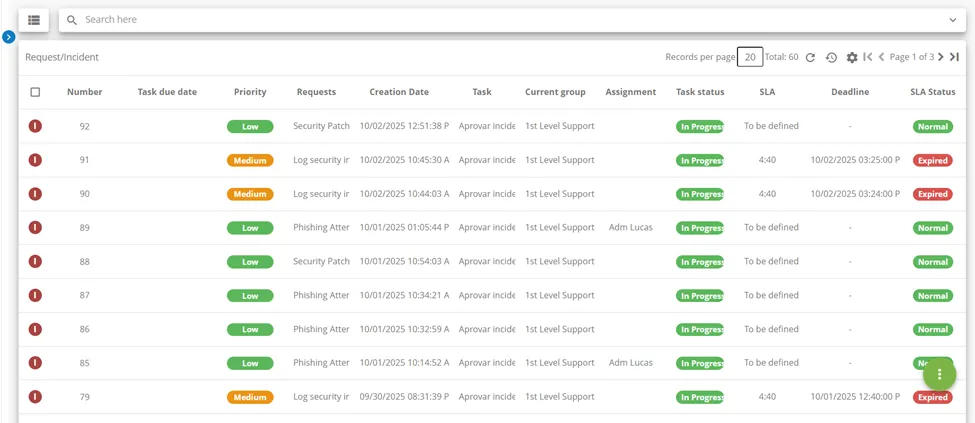
The platform use the incident management to log and manage incident records based in user ID.
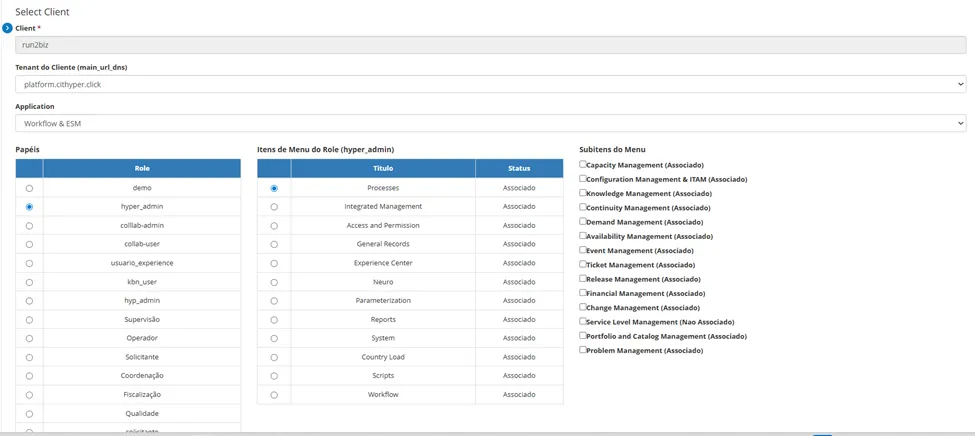
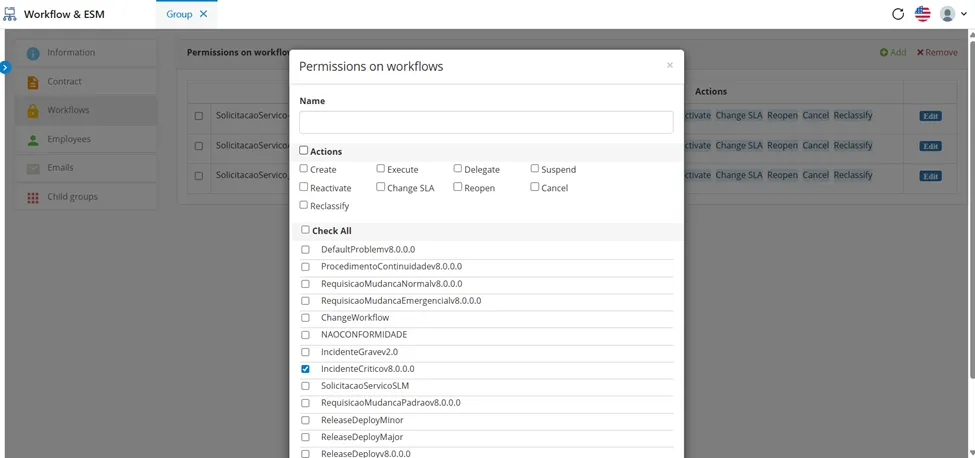
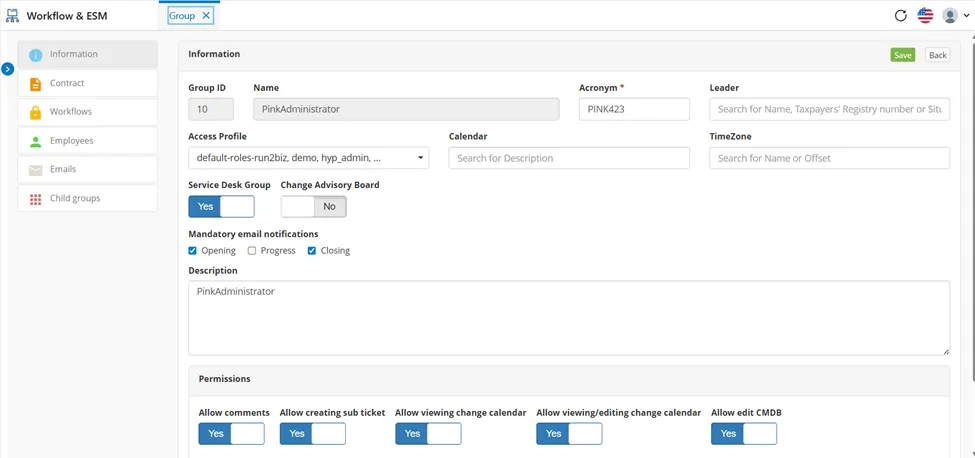
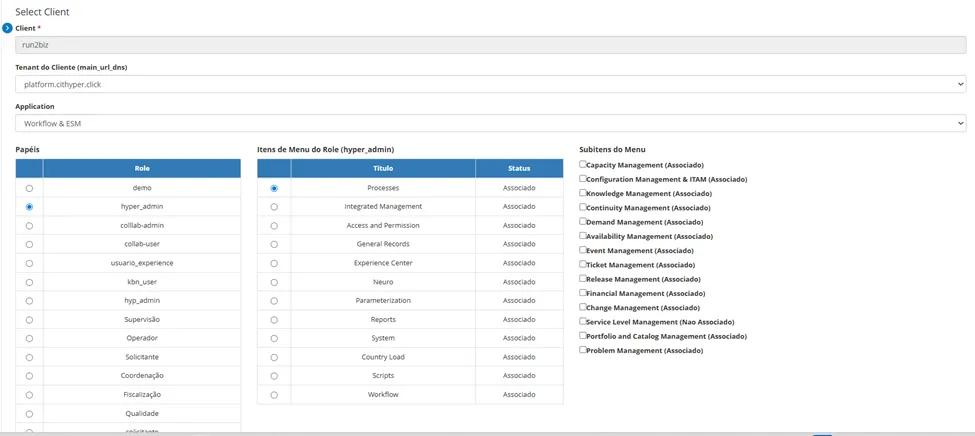
The roles can be defined on user, group or process
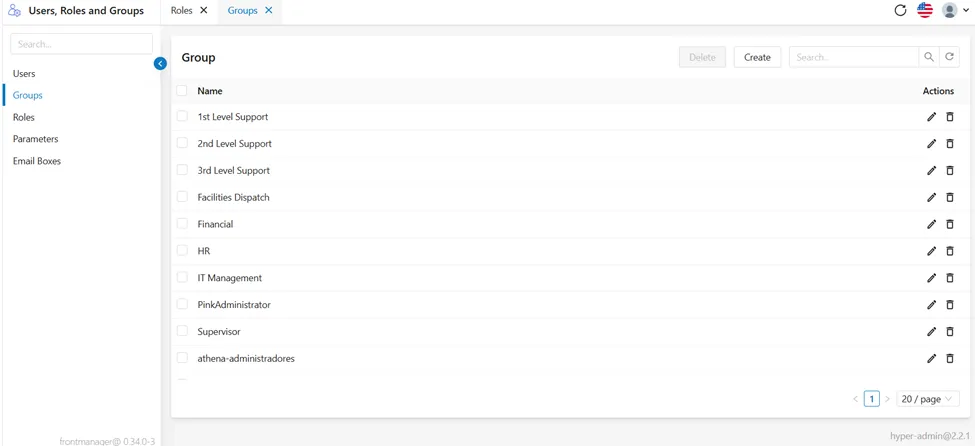
Process
Incident Queue
Based on RBAC security process defined on IAM, the administrator can define the user access for each process
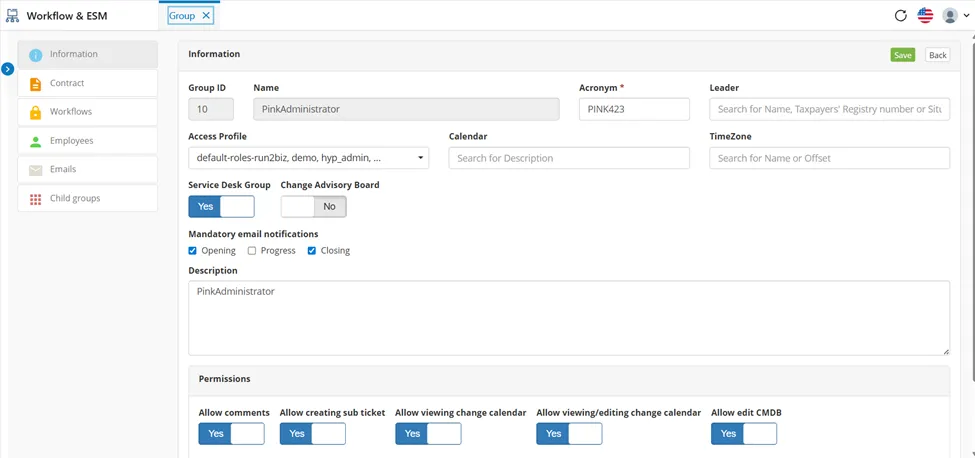
Even on global search
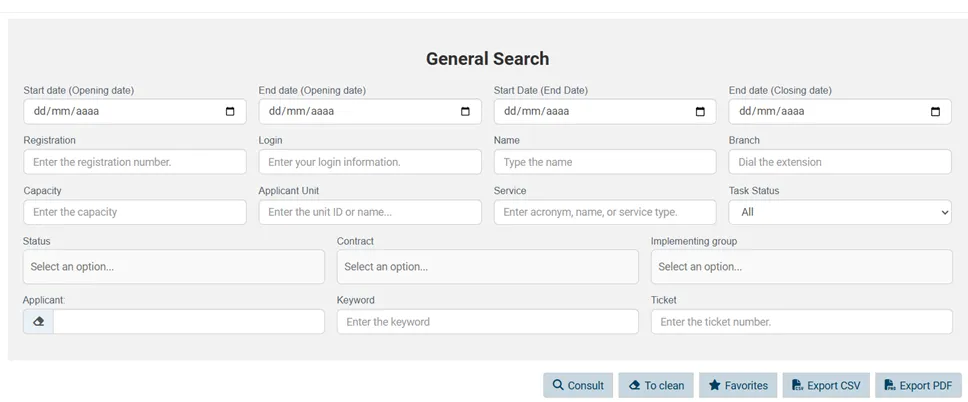
Each workflow need to be linked in specific process to orchestrate the workflow, and process hold the RBAC permissions and roles.
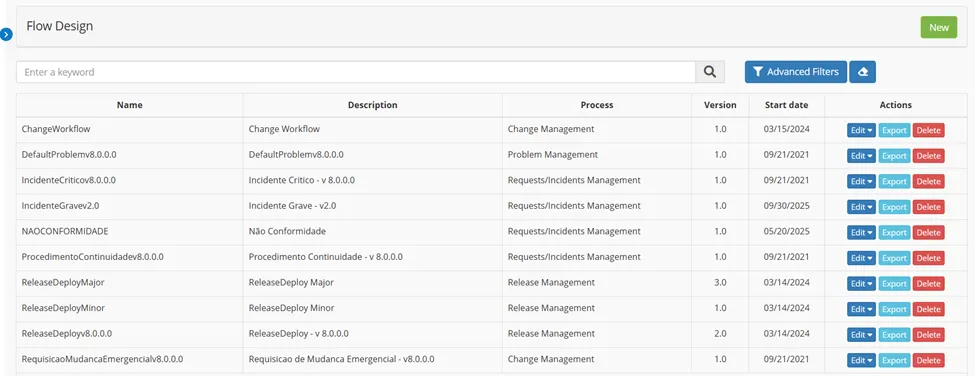
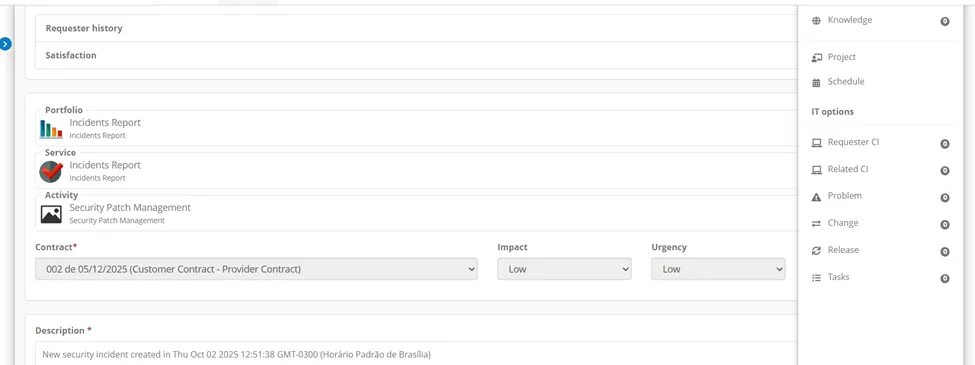
In Lowcode integration flow all external integrations with antivirus and patch platform can be configurated/create and used on workflow process. The integration flow create integrations as component that can be orchestrated thought process flow.
First eval the administrator need to create an integration workflow using lowcode capabilities or use pre-defined antiviruses component. After create the component, all integration will be done and ready to use in workflows that support all practices
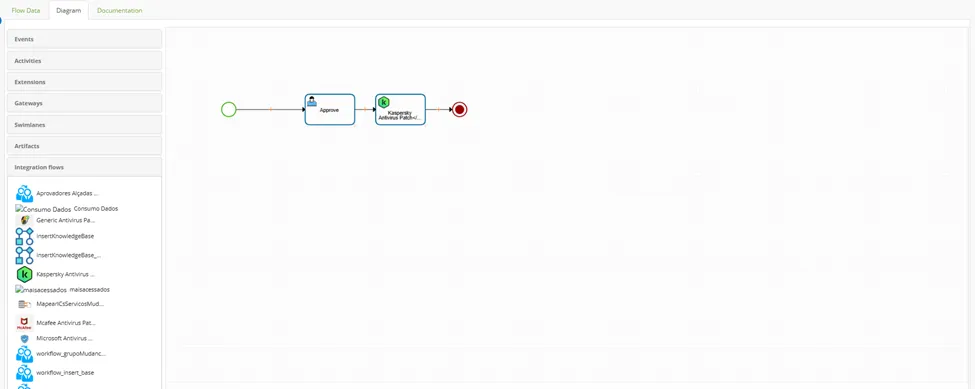
On workflow, just drag and drop the antivirus component that company use, and apply. Done! All deploy based / came from request/incident will be performed using antivirus integration
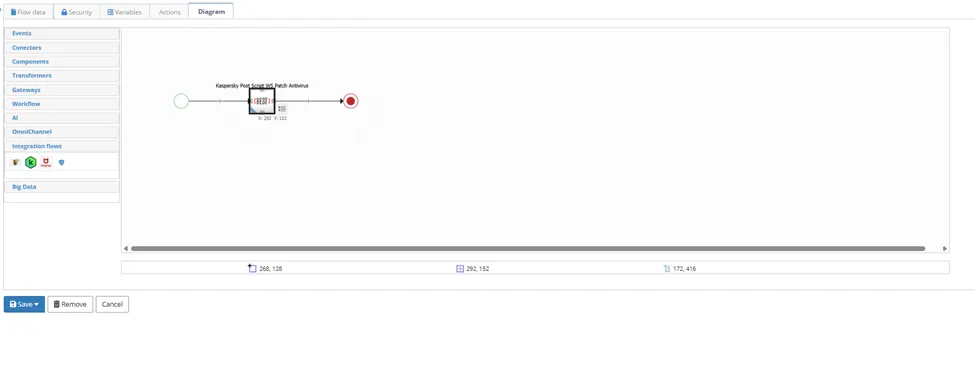
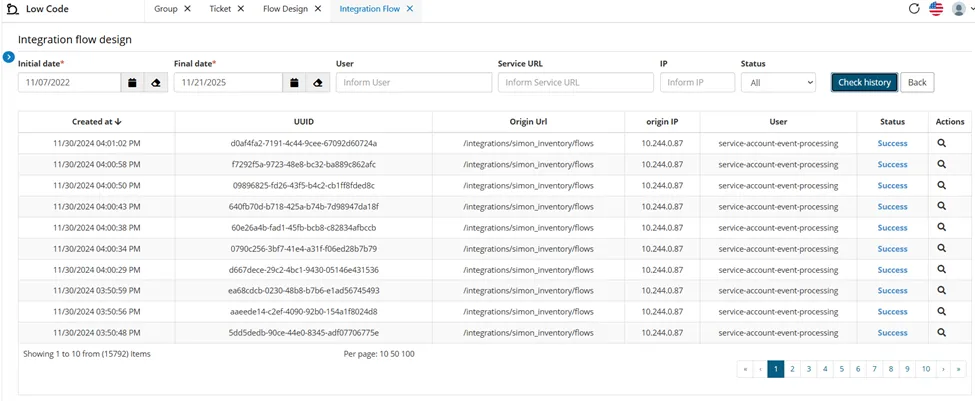
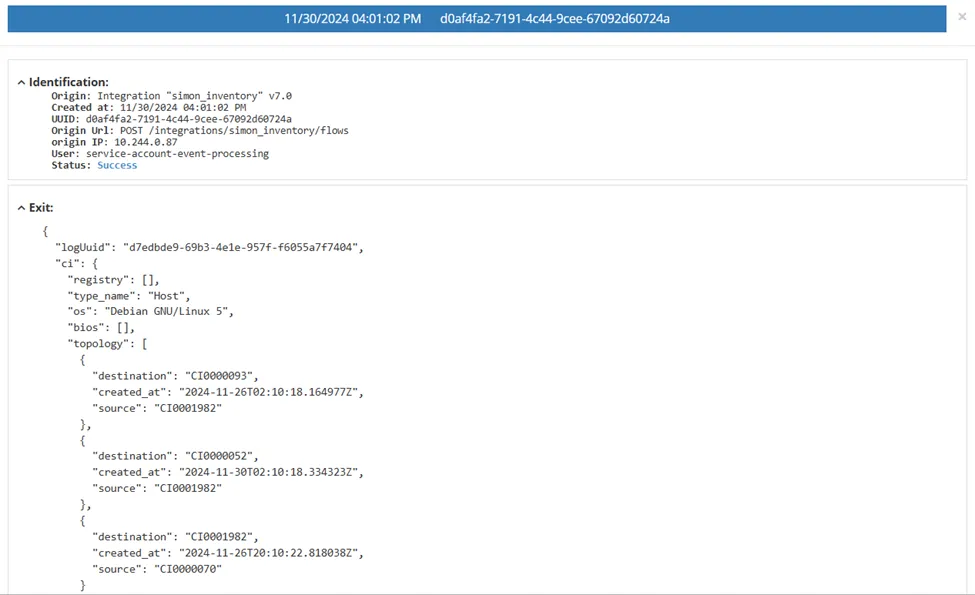
The integration flow create integrations as component that can be orchestrated thought process flow and all process can be supported, enables the management of security patch and virus update schedule, history, reported on started via incident process or Ai Agents.
Based on RBAC security process defined on IAM, the administrator can define the user access for each security process.
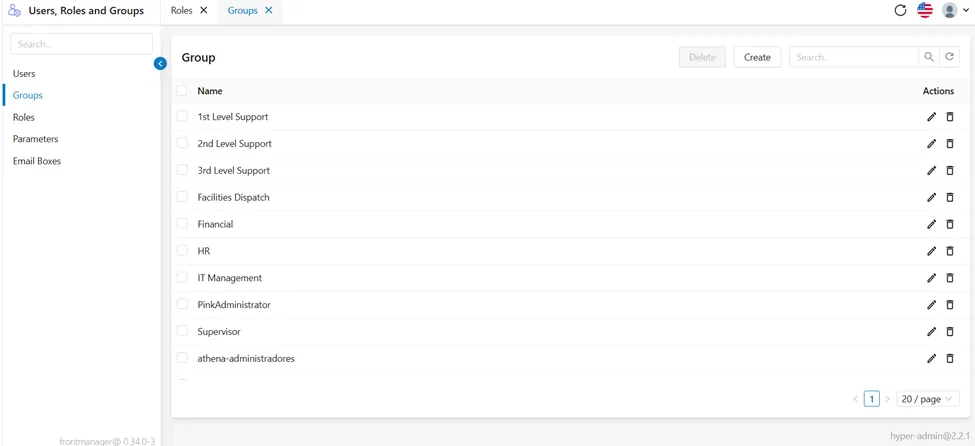
Defining the Process Access and roles
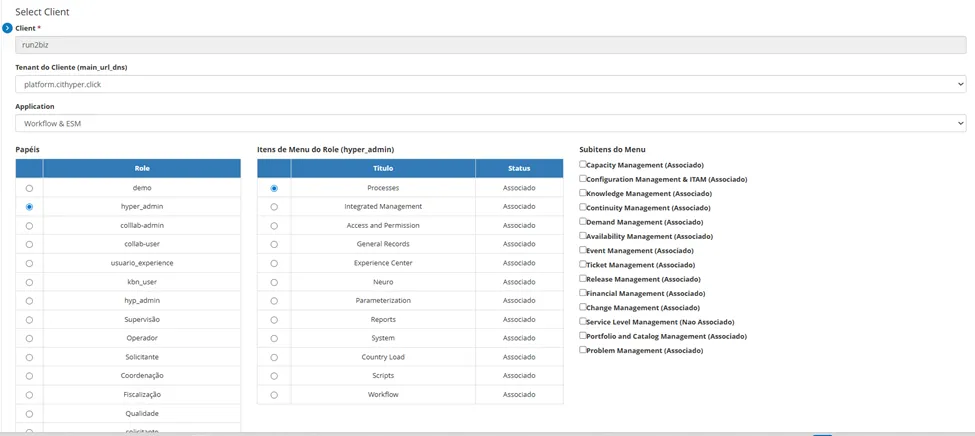
Defining actions for each role/group x process
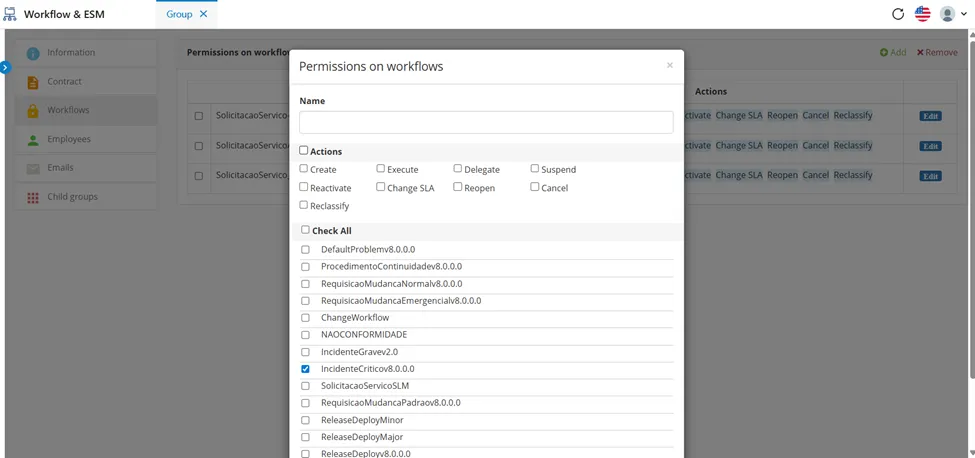
Based on RBAC security process defined on IAM, the administrator can isolate designated service component records as secure items and restrict access for view and updates.
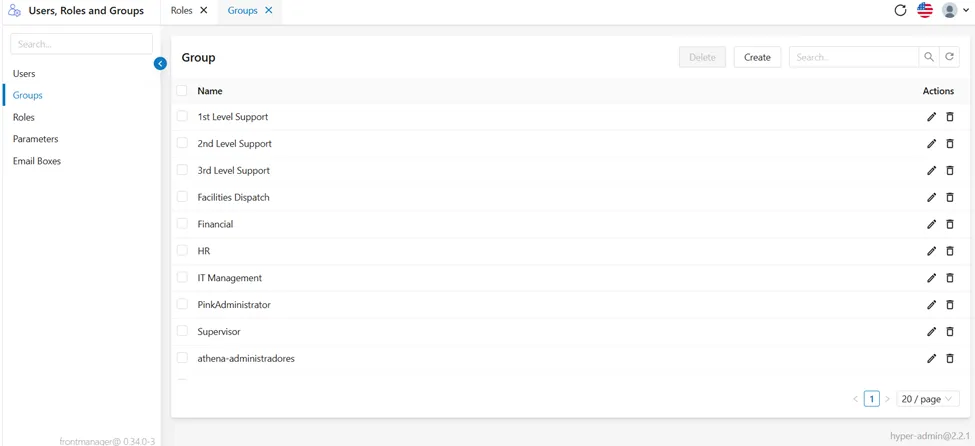
Isolating service component records and Restrict Services
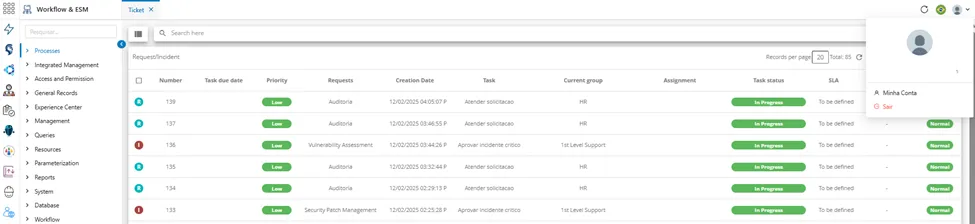
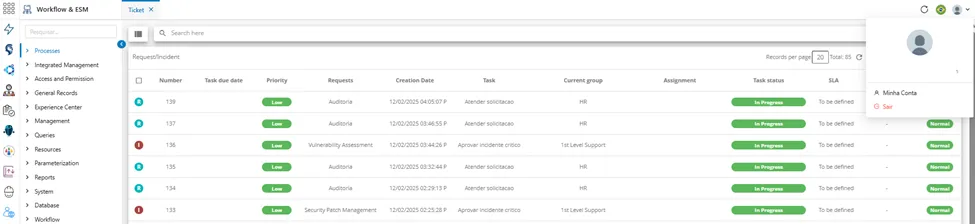
Based on ID/Roles the user can access specific services and Incident, Request, Change and Problem portfolios.
Incident, Service Request
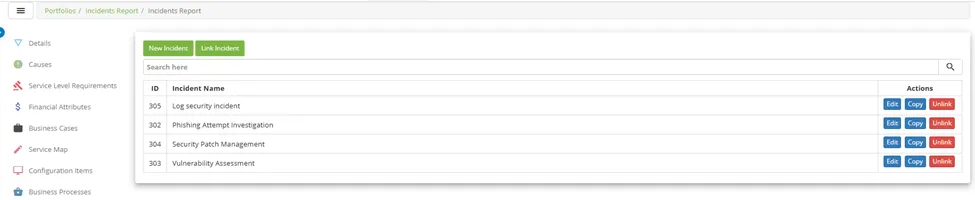
Change
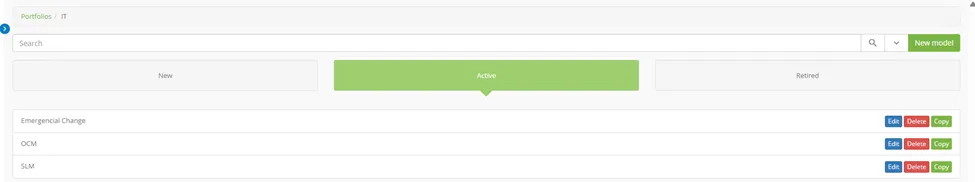
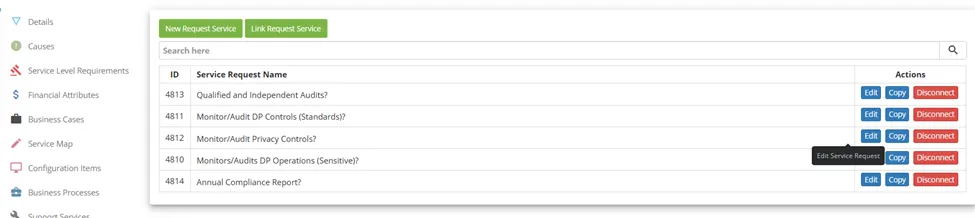
The security requirements can be configurated on RBAB/IAM to provide access on SLM Process and services published on the service catalog
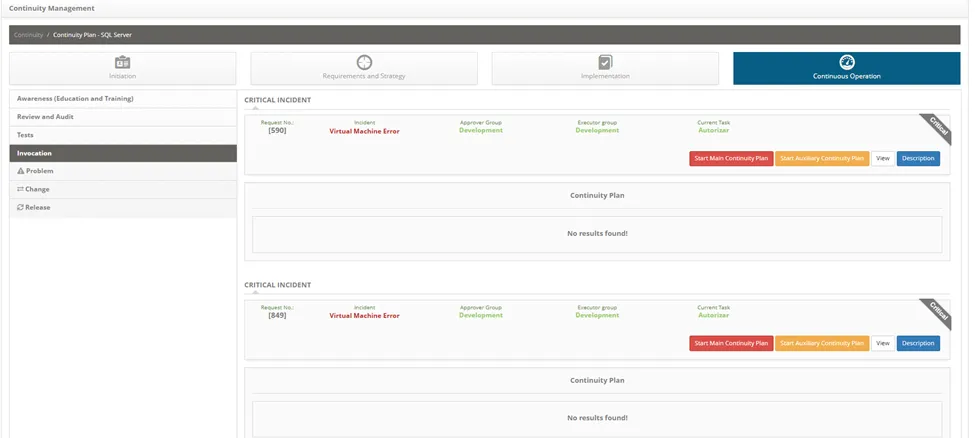
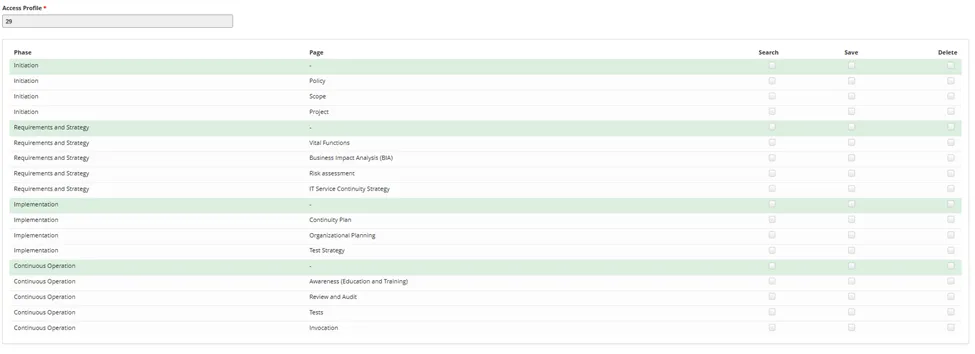
On Continuity Process can be defined all permission access. The continuity process can be triggered only by user authorized on IAM.
Using the security system RBAC/IAM administrators can assign risk ownership to designated persons, and limit access to risks and the register based on user ID/role.
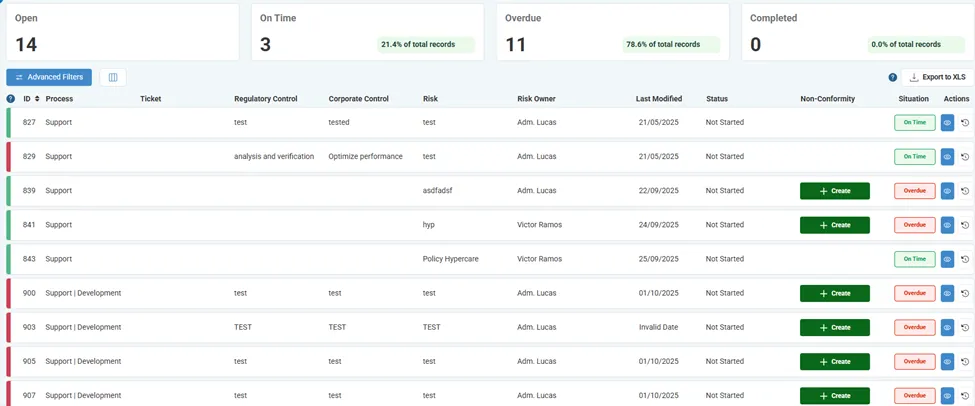
Defining the Risk Owner based on roles
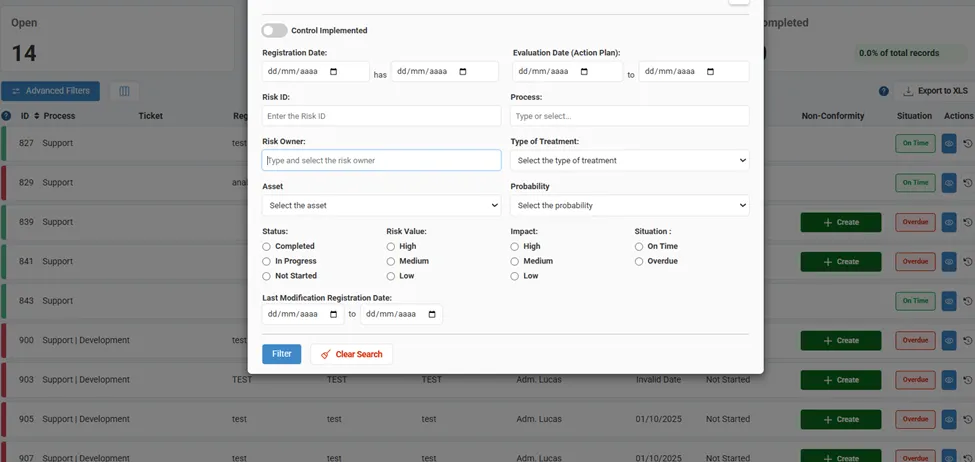
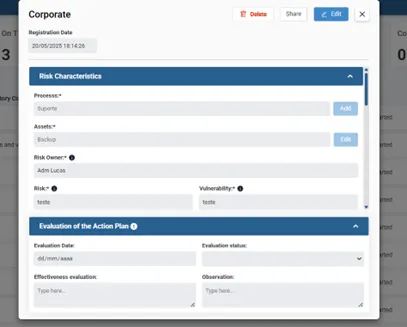
Each risk can be linked with Knowledge Base Protocols and IT Asset Controls:
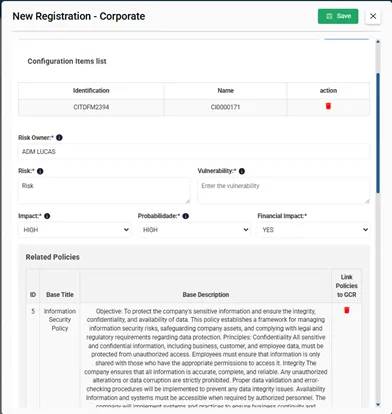
When the platform found some discrepancy o asset baseline, triggered the security incident with all discrepancy found.
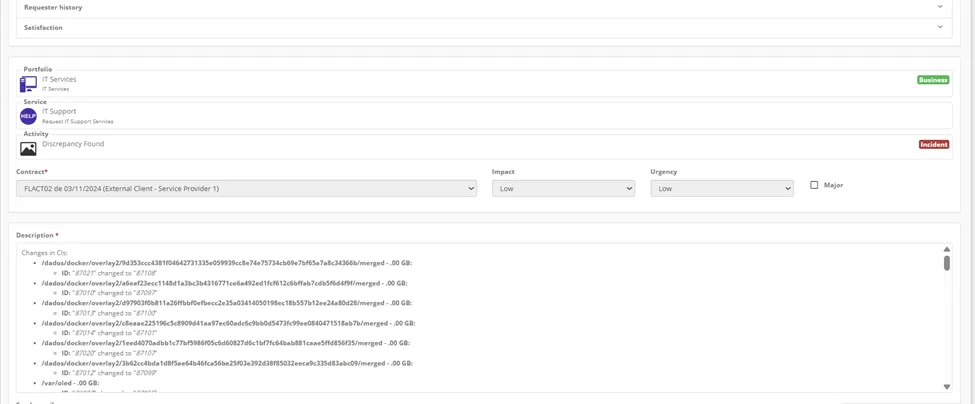
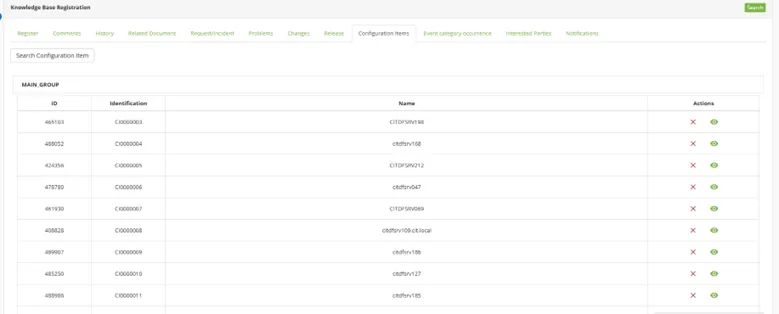
Risk Management can link with CMDB and trigger an incident regarding all security roles and workflow process/tasks.
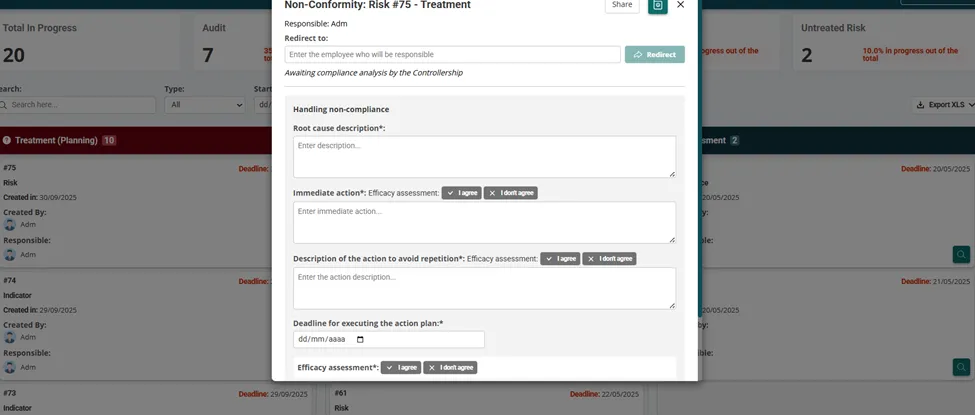
Using the knowledge base all information, documentation of, or links to security and compliance requirements, policies, related controls, statutes, regulations, citations, and enables the necessary communication can be create and defined using the security id/roles
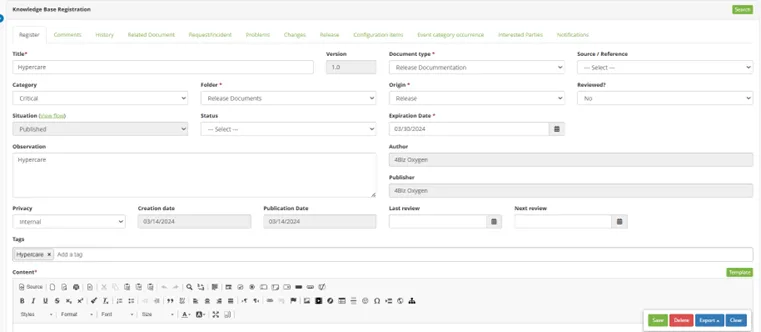
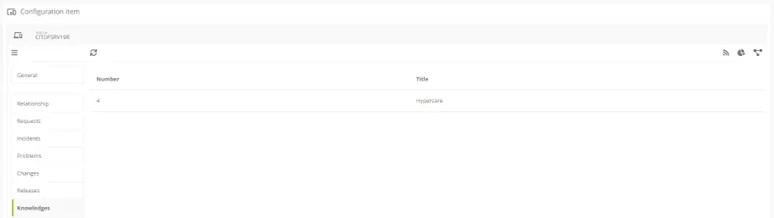
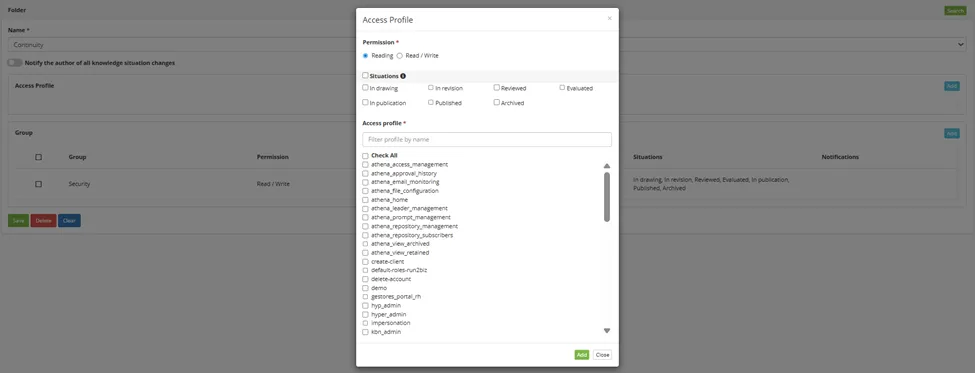
Risk and NonCompliance management system can manage, report the compliance with security requirements, controls, policies, statutes, regulations, and citations
Risk Management
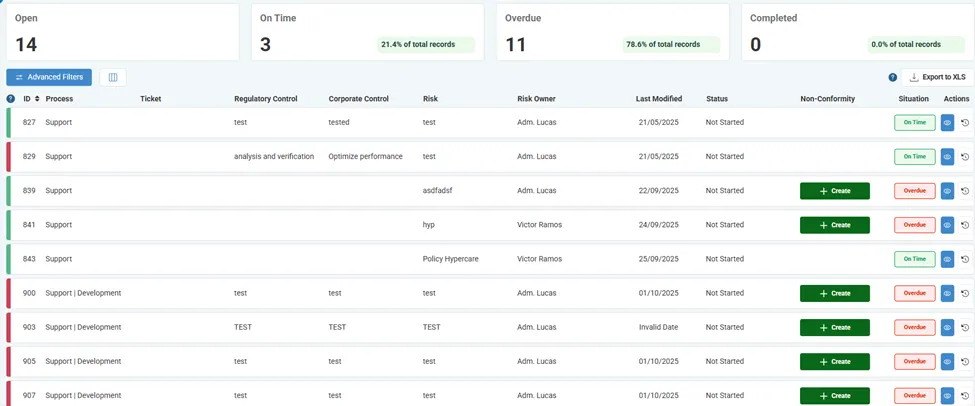
Risk Managed
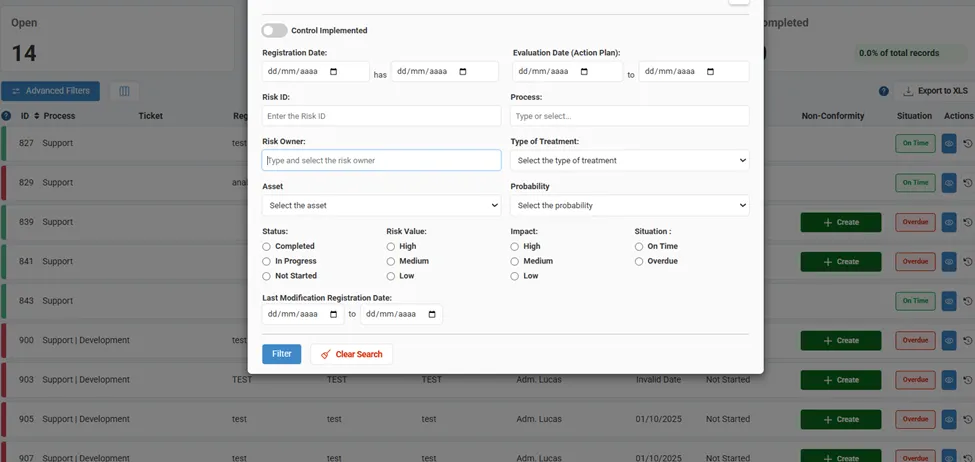
Nonconformity Process – Treatment Risk
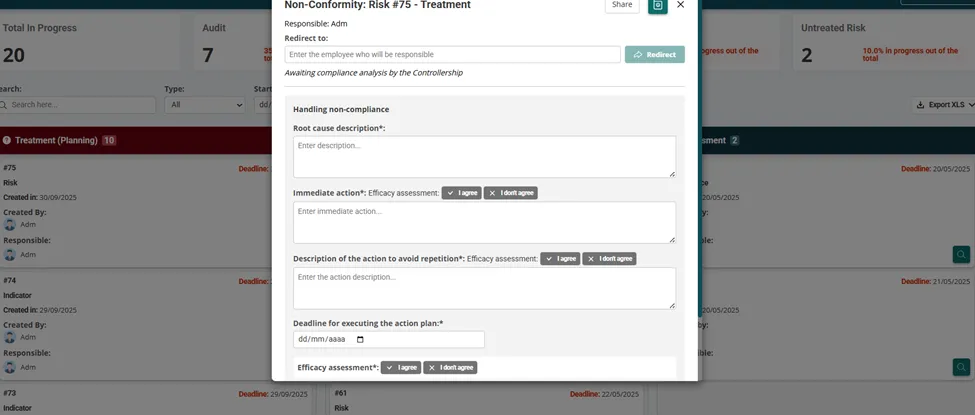
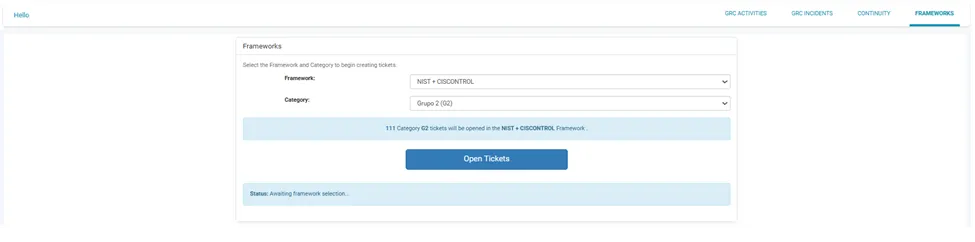
The Security department can pick a specific framework such as Ciscontrol, Nist, Iso, GDPR, LGPD or internal audits and reviews to trigger audit tasks for each responsible.
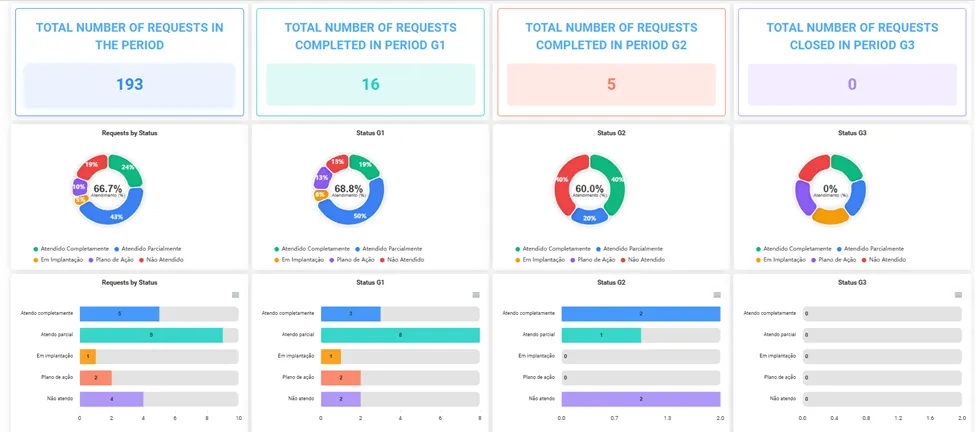
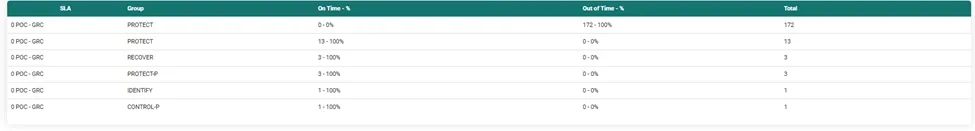
All access and policies are managed via the IAM definition and polices
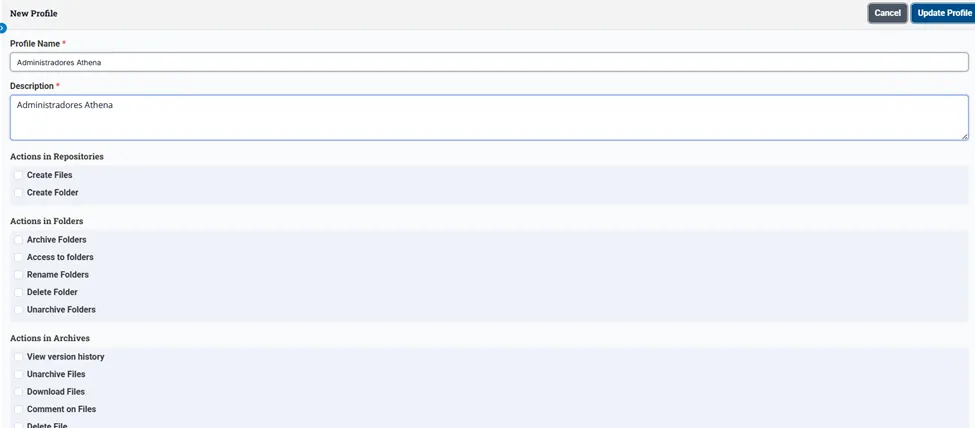
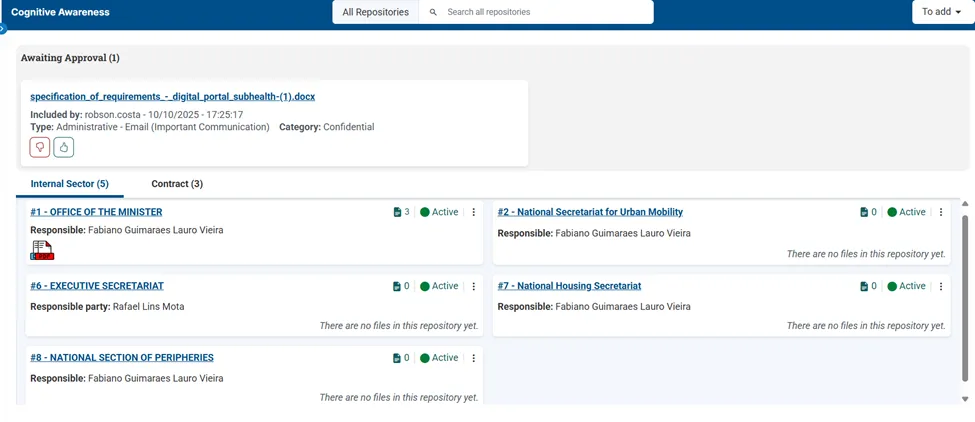
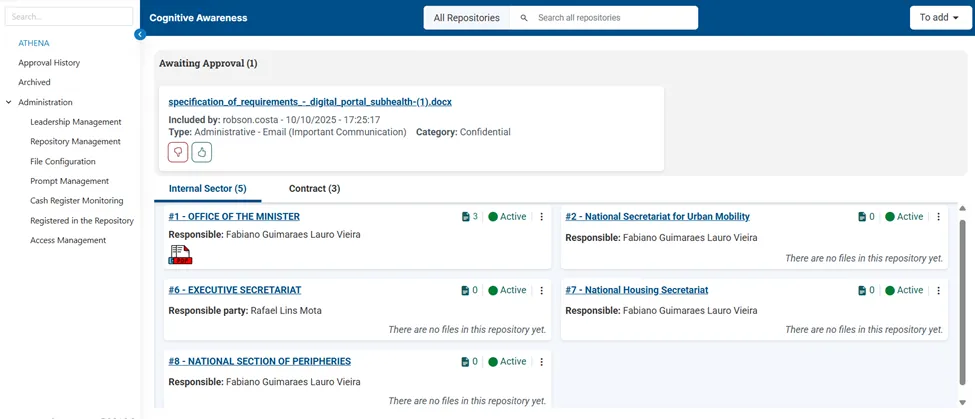

Workforce Management provide all job codes and references that can be handle vy security area, checking the profiles, roles and if needed can trigger the incident or request based on audit statuses.
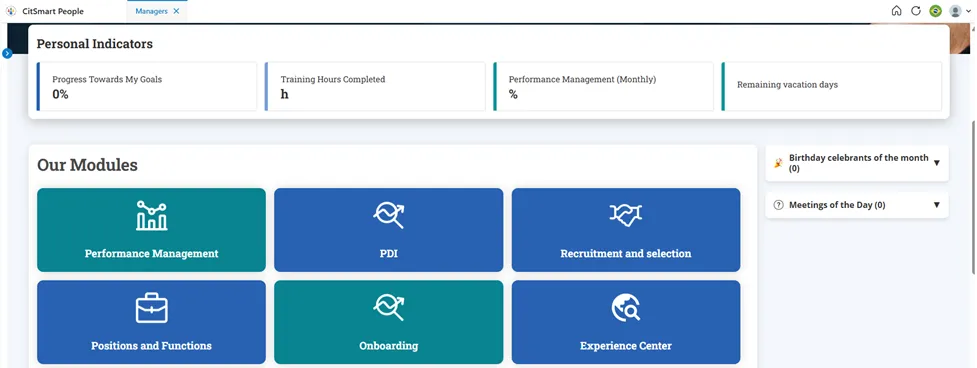
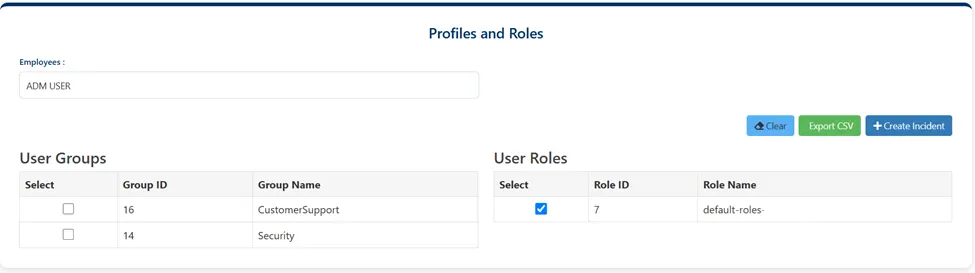
User profile audit
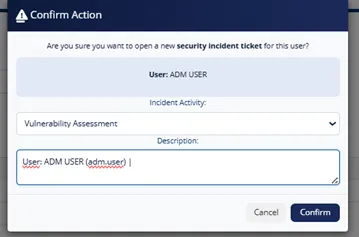
The platform can trigger the incident or request based on audit statuses all necessary support and audit workflows/tasks for system, application, and data access issues, as well as non-compliance based on IAM requirements
Profile Audit
Trigger incident
Incident Created